Synology NAS devices could be attacked by a new ransomware threat, so update now
follow us
Add us as a preferred source on Google
- Synology warned of active ransomware attacks exploiting long-patched DSM vulnerabilities in outdated NAS devices
- The attackers are reportedly deploying the C3rb3r cipher and demanding thousands of dollars in ransom.
- Users are urged to patch immediately, restrict Internet exposure, and secure access to the NAS to avoid compromise.
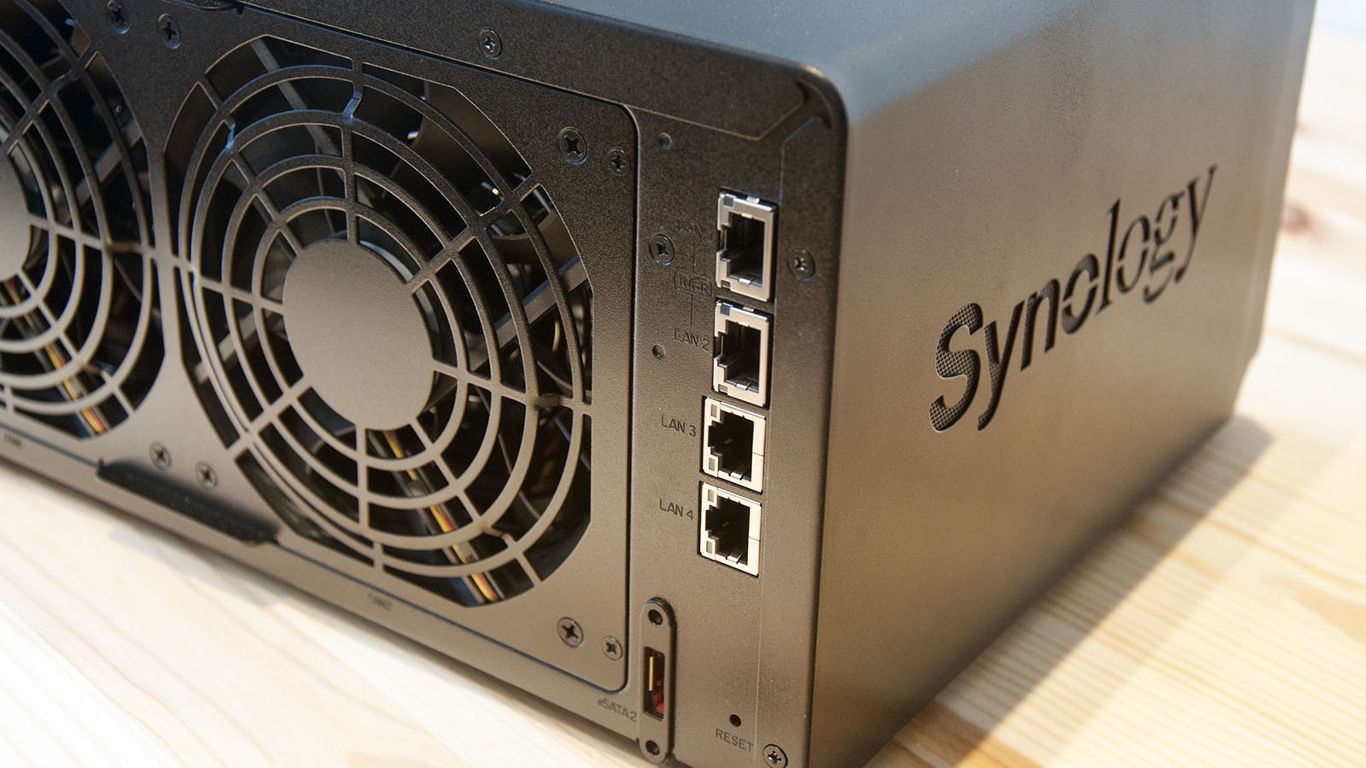
Synology, a major network attached storage (NAS) manufacturer, is warning users about continued ransomware attacks targeting devices running outdated software. He urged all users to apply the provided patches and protect their devices without delay.
In a brief announcement, Synology said it “identified threat actors exploiting a vulnerability patched in December 2024 to target devices running outdated versions of DSM.” The goal of the attacks appears to be data encryption and demanding a ransom.
“Synology strongly urges all users running vulnerable versions to update DSM immediately to protect their systems. Synology also recommends enabling automatic updates to keep DSM up to date at all times.”
Latest videos ofTechnologyRadar
C3rb3r attacks
The ad is pretty stingy on details. We don’t know what vulnerability threat actors are exploiting, where exactly, or how successful they are.
We also don’t know how many devices are at risk: the Shadowserver Foundation tracks a total of 380,000 endpoints connected to the Internet (many of which, most likely, are running the latest version of the software and are therefore protected).
The company also did not say who the threat actors are, but according to beepcomputerThere has been a “massive wave of reports” of Synology customers whose data was apparently locked by the “C3rb3r” encryptor. These customers were asked to pay “thousands of dollars” in ransom in exchange for the decryption key. The publication says the first reports began to emerge more than two weeks ago.
There are two main ways for cybercriminals to access an electronic device and encrypt the data there: either by exploiting a zero-day vulnerability (one that has not yet been patched) or by exploiting years-old n-day vulnerabilities (those that were patched months ago) on devices that have never been updated or secured.
With Synology users, the latter seems to be the case. The company said attackers were exploiting a vulnerability patched in December 2024 and linked to a security advisory from November 2024, which listed three fixed bugs: CVE-2024-10441 (arbitrary code execution), CVE-2024-50629 (reading arbitrary files), and CVE-2024-10445 (a bug that allows writing files to compromised devices).
DSM 7.2.2 owners should upgrade to 7.2.2-72806-1 or higher, DSM 7.2.1 to 7.2.1-69057-6 or higher, and DSM 7.2 to 7.2-64570-4 or higher. DSM 7.1 should be updated to 7.1.1-42962-7 or higher, while those running DSM 6.2 to 6.2.4-25556-8 or higher. Only in the latest version, 6.2, the vulnerability is labeled as “moderate.” In all other cases it was considered “critical”.
Why are NAS devices attacked?
NAS devices are dedicated storage systems that businesses can connect to their local network and allow employees to access, share, and manage files stored in a centralized location. They are quite popular among SMBs that lack the resources to maintain more complex enterprise storage infrastructure.
In addition to being used as a kind of hybrid cloud, NAS is also used to store business documents and often acts as a centralized backup. Relatively low cost, easy deployment, and easily expandable storage capacity make NAS devices an attractive alternative to both dedicated file servers and cloud storage subscriptions.
However, this also makes them a valuable target for cybercriminals, as we have seen in this case of Synology. The best way to defend against ransomware attackers is to completely remove the NAS from the public Internet or at least limit access to a handful of vetted identities. It is also recommended to keep devices updated with the latest firmware and software.
It’s worth mentioning that NAS devices typically come with RAID redundancy and built-in backup features, but they don’t necessarily protect against ransomware that encrypts stored data.
The best antivirus for all budgets
Follow TechRadar on Google News and add us as a preferred source to receive news, reviews and opinions from our experts in your feeds.
Post Comment