FBI leads action to shut down bulletproof service Virtualine linked to major cybercrime activity
follow us
Add us as a preferred source on Google
- The FBI and its international partners seized infrastructure linked to Virtualine, a hosting provider that allegedly provides services to cybercriminals.
- Authorities say the service facilitated phishing operations, ransomware, illicit crypto activity and other crimes.
- Investigators seized servers and customer data, although no arrests have been announced so far.
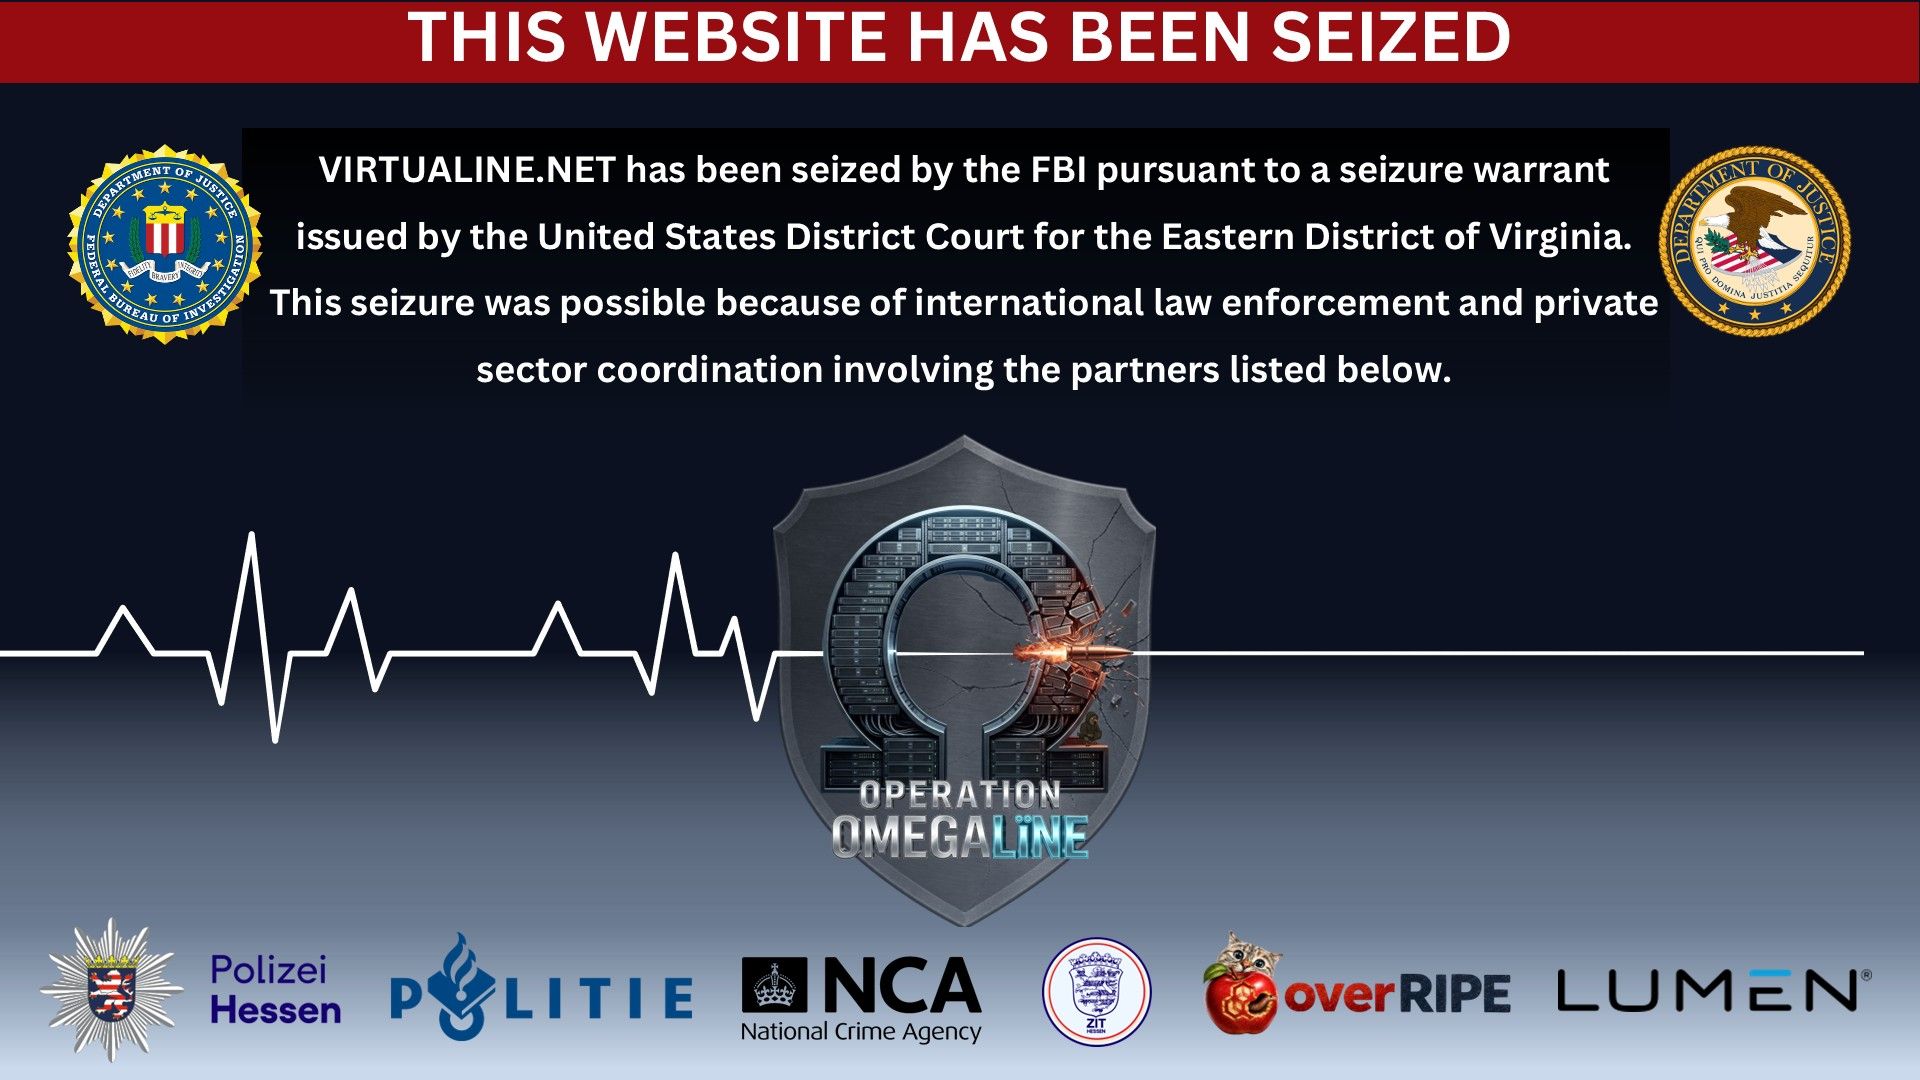
The FBI announced that it seized the website of Virtualine, a bulletproof hosting service that allegedly enabled child pornography, laundered stolen cryptocurrency and extortion, and facilitated a wide range of other criminal activities.
The operation was carried out in collaboration with German and Dutch authorities, as well as several private companies, with police raiding a data center in Limburg to seize “dozens of physical servers” that also housed “hundreds” of virtual servers. As a result, they gained access to information on more than 3,000 Virtualine customers, it was said.
“The police are currently taking follow-up action towards these users,” Dutch police said, although it is difficult to say how valuable the information will be, as most bulletproof hosting providers do not ask for private data and criminals are also good at hiding it.
Latest videos ofTechnologyRadar
Bulletproof accommodation
Every website, including hacking forums, criminal service providers, and even scam landing pages, needs a server to host it. Hosting providers who rent these servers generally comply with law enforcement authorities, so when the police request a takedown or file a complaint, most comply. However, there is a subset of accommodation providers, colloquially called “bulletproof accommodation”, that are unusually resistant to pressure from authorities.
It doesn’t mean they are all inherently illegal or malicious. There are cases where these services are necessary: in countries with strong censorship or where website owners want to protect their identities.
In this case, however, Virtualine was overtly criminal, and the US Department of Justice (DOJ) said it advertised its services to criminals on cybercrime forums saying, on at least one occasion, “You can use Virtualine for all illegal/black hat activities (including phishing).[h]ing, carding, email spam, port scanning and all others) except children’s content and terrorist activities.”
The company went one step further. In March 2026, it introduced an “additional protection plan” that offers customers who receive removal requests “another shell company not affiliated with Virtualine, after which the server is reactivated.”
Interestingly, Virtualine said it did not accept child pornography or terrorist content, but according to the Department of Justice, it did the exact opposite.
One of its clients created a forum that allowed users to post and sell access to “nude, sexually suggestive and/or sexually explicit images and videos of minors and adults,” while promoting a contracted hacking service that broke into people’s accounts and stole their explicit photos and videos. Virtualine was even notified about it by law enforcement agencies in Germany, Canada, and Australia, but decided to ignore the warnings and continue hosting the client.
At the same time, Virtualine customers were allowed to pay in Bitcoin, offering a non-hosted Bitcoin address that allowed customers to “make direct payments without worrying about their funds being flagged as illicit.” Citing data from Chainalysis, beepcomputer said the company’s wallet was seen receiving funds from ransomware operations, information thieves, Russian-language cybercrime forums, and more.
“Virtualine then laundered those profits to hide their origin,” the blockchain company added.
Drilling the kevlar
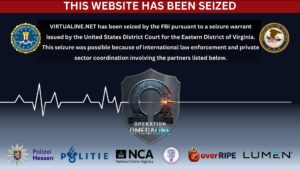
In addition to seizing servers and data, the main website, virtualine.net, was defaced and now displays the usual FBI message “this website has been seized.” Unfortunately no arrests have been made, meaning the service will most likely continue to operate.
According beepcomputeris “partially online”, but its network prefixes currently have very low routing visibility, which could mean that much of its infrastructure has been taken offline.
Typically, outages like this are only temporary and it won’t be long before they are fixed and the service is fully operational again.
The best antivirus for all budgets
Follow TechRadar on Google News and add us as a preferred source to receive news, reviews and opinions from our experts in your feeds.
Post Comment