Scammers target new students by hijacking legitimate emails from US universities
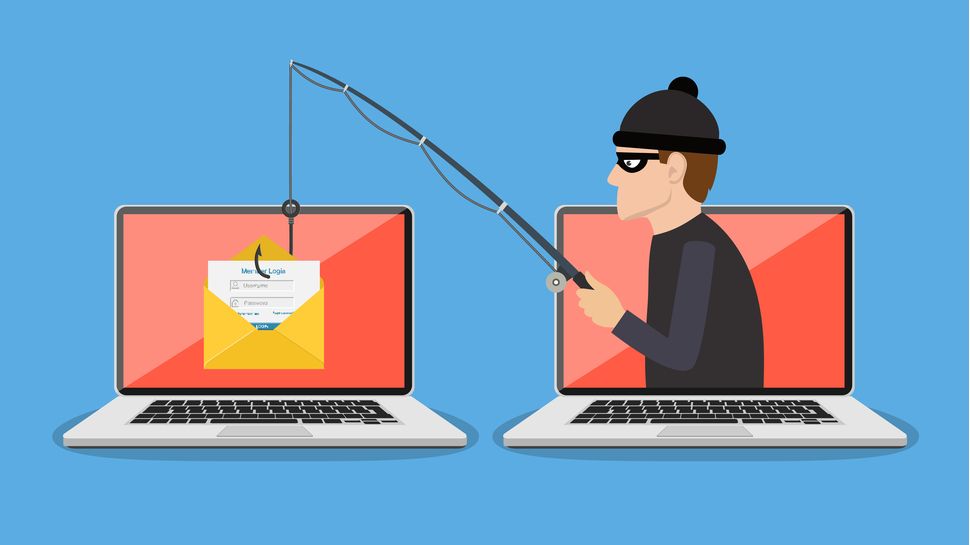
- Stolen .edu Accounts Spread Fake Job Offers and Gift Card Scams
- Victims deposit fake $1,000 checks, then purchase gift cards from scammers
- Proofpoint linked operators to Nigeria through intellectual property registration investigations
Nigerian cybercriminals are targeting Western university students with an Advance Fee Fraud (AFF) scam that tricks them into giving away hundreds of dollars.
Security researchers Proofpoint discovered the campaign, which aims to get gullible students to buy gift cards with their own money and send them to scammers.
We don’t know how many people were victims or how long the operation lasted, but Proofpoint believes it knows why scammers primarily target college students.
Latest videos ofTechnologyRadar
What is the scam?
“Younger students may have less experience with email correspondence and are new to engaging in potential job or money-making opportunities; alumni may have active email accounts but not use them frequently, giving threat actors the opportunity to hijack their contact lists; and staff and faculty constantly receive communications from students, parents, community members, etc. from a variety of personal and university emails,” the experts said.
“By gaining access to a .edu account, threat actors can use the authority of the TLD to lend credibility to their scams both inside and outside the target organization.”
The scam has several stages. It begins with a phishing email to anyone with a .edu address, warning the victim that their email account will be deactivated due to a made-up excuse such as retirement, graduation, or transfer. The honeypot asks the victim to “verify” their address and, in doing so, they are also asked to share their passwords.
After gaining access to the account, the criminals use it to share a second phishing email, this time with students in the contact list, as well as anyone else with a .edu address. This lure advertises a fake job that students can apply for. Those who “get the job” are given a copy of a check for $1,000 and asked to deposit it. They are told to keep half their salary and buy gift cards with the other half, which they must then send back to the scammers.
The checks are obviously fake, and by the time the bank discovers the scam, the victim will have already purchased the gift cards and sent them. The bank then reverses the deposit, leaving the victim $500 short.
Proofpoint researchers were “hired” for one of these jobs, and thus discovered the entire modus operandi. They also learned that if the victim does not follow instructions, they will become aggressive, suggesting different payment services and even calling the victim on the phone, posing as an FBI agent, threatening them with legal action and arrest.
Nigerian operation
Attributing the scam to a particular group is quite difficult, investigators said. However, they managed to trick the scammers into using Grabify, an IP logging and URL shortening service commonly used by online marketers.
The links are used to extract things like device information and IP addresses from whoever clicks on them, and Proofpoint researchers found that the interaction comes from Nigeria.
While there are ways to hide the IP address, Proofpoint is quite confident in the location of this particular operation.
“While it is possible for threat actors to spoof their infrastructure, based on our investigations of hundreds of compromises, these AFF scammers typically use their real mobile network infrastructure to carry out their crimes. Even if scammers use a VPN, they often still click on researchers’ links from their genuine devices due to the cross-platform communication style they use (and desire to monetize, despite potential deanonymization),” Proofpoint concluded.
The best antivirus for all budgets
Follow TechRadar on Google News and add us as a preferred source to receive news, reviews and opinions from our experts in your feeds.
Post Comment