Hackers Claim to Have Attacked Thousands of Trump Phone Customers as Bad News Continues for Gold Smartphone Fans
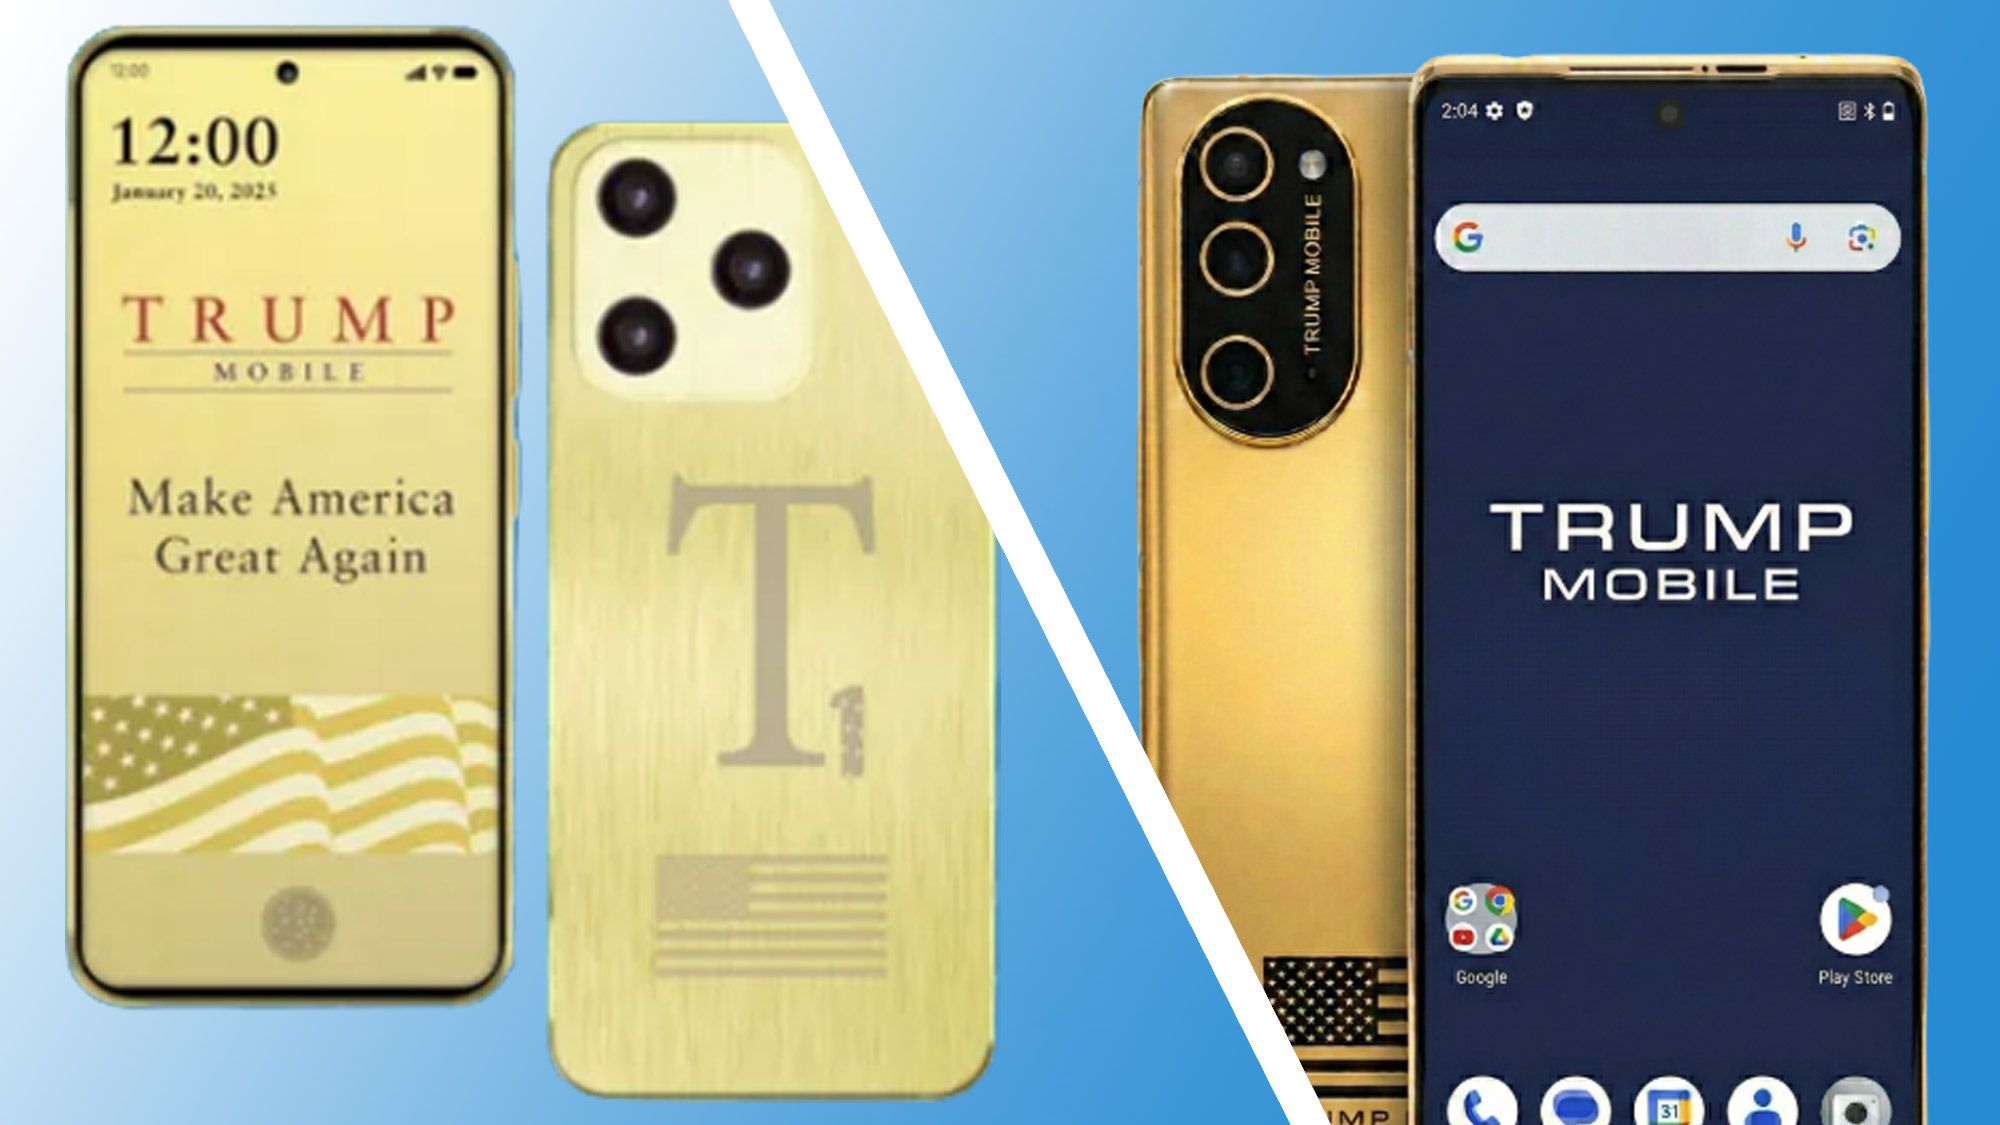
- The BYOD cybercrime group has released records of 3,615 Trump Mobile customers, including names, home addresses, phone numbers and order details.
- BYOD says it entered through malware on a Liberty Mobile employee’s device and was told by Trump Mobile that there was “no team” to respond.
- The published data appears to cover wireless service rather than T1 phone orders, and includes abandoned records and the Trump Organization’s own CIO.
A newly formed cybercrime group calling itself BYOD says it has stolen and published personal data belonging to 3,615 Trump Mobile customers, the latest setback for the Trump-branded wireless company and its gold-colored T1 smartphone.
straight arrow news first reported the breach after reviewing the data set, which contains names, email addresses, phone numbers, addresses and order details, and contacting the people listed in it.
Trump Mobile has not responded to straight arrowand neither the Trump Organization nor Liberty Mobile, the Florida-based carrier behind the service, responded to questions from The Registry.
Latest videos ofTechnologyRadar
A ransom note that skipped the ransom component
BYOD published the data on its dark web leak site in late September 2026; A ransomware tracker cited by IBTimes UK dates the entry to September 29. The Registry describes BYOD as a new ransomware-as-a-service operation, although Trump Mobile is only the third organization named on its site IBTimes United Kingdom points out that nothing published so far shows encrypted systems or a ransom demand.
The group’s account of how it got in is broadly consistent, even if the details differ slightly: BYOD told International Cyber Digest that it compromised a Liberty Mobile employee with an information stealer, while Cybernews and Android Authority describe a remote access trojan.
Regardless of how they accessed the device, the BYOD messages indicate that it moved from that foothold to Trump Mobile’s exposed subdomains, still has live access to a customer dashboard, and claims that neither company used multi-factor authentication.
As proof, he sent straight arrow a screenshot of the dashboard showing a customer’s personal data, but such access has not yet been independently confirmed. The most damning part of this is that Trump Mobile’s response to this has been “We don’t have any equipment to handle this” and calling anyone who hacked it a terrorist, an exchange that BYOD claims took place.
The data, however, has been maintained; straight arrow reached people who confirmed that their data was accurate, cyber news said his samples appeared genuine and did not match previous violations, and PCMag It reached three people in the file, one of whom was surprised to find an accurate record of canceling a 30-day unlimited plan.
BYOD may not even be the first to cash in: A separate group, EndZone, claimed on September 23 to have taken data from 4,000 Trump Mobile users. IBTimes United Kingdom reports, and security researcher Dominic Alvieri said The Registry the EndZone dump “appears to be the same original violation.” BYOD denies a formal link, and a representative tells you PCMag that one member “only knows a few people behind EndZone,” according to IBTimes United Kingdom.
At its launch in June 2025, Eric Trump promised that “Trump Mobile is going to revolutionize mobile phones,” but what followed has been less revolutionary.
The “Made in America” promise disappeared from the website within two weeks. Shipping moved from August 2025 to December, then March, then April, and in April the company rewrote its pre-order terms to state that “a deposit is not a purchase.” In January, lawmakers urged the FTC to examine the brand’s marketing.
For consumers, there is a silver lining: no payment card data has been reported in the landfill, so the immediate risk is phishing rather than outright fraud. However, this doesn’t completely solve the problem: names, phone numbers, home addresses, and order histories are exactly what scammers need to convincingly pose as a carrier or delivery service.
Anyone who has signed up, or just started signing up, with Trump Mobile should treat unexpected messages about orders, refunds or account issues with suspicion at a time when Trump Mobile continues to drag its feet on the matter, much like its breach in May, when the company said it was still deciding whether to notify people. However, this time it’s a little different: he hasn’t said anything at all.
Follow TechRadar on Google News and add us as a preferred source to receive news, reviews and opinions from our experts in your feeds.
Post Comment